


Level 1: EU & UK legislation
Primary law, including DORA, MiFID II, AMLR, and MiCA


Purpose-built for risk and compliance teams. Scale your business without the risk
 +
Track and assess EU, UK, and member-state legislation, including supervisory guidance
Map obligations to policy, systems and controls, then remediate in one system
From AMLR to DORA, assign key controls, collect evidence and monitor continuously
Primary law, including DORA, MiFID II, AMLR, and MiCA
Regulatory and implementing technical standards under Level 1
Guidelines and Q&As from the European supervisory authorities


Member-state rules and supervisory guidance


 +
Don’t see what you require?
Book a call and tell us your requirements, we can get it sorted
Integrations





Enter new markets and stay compliant
Launch new products without the risk
Navigate nuanced scheme rules
Handle prudential and conduct obligations
Umbra meets the demands of any regulated financial firm
Umbra is committed to rigorous international safety and security standards
Umbra is DORA compliant, aligned with the EU standard for operational resilience
We operate under GDPR — the world’s strictest standard for data privacy
Working toward ISO 27001 certification, the standard for information security
In progress
Working toward secure and compliant management of data across all our systems
In progress
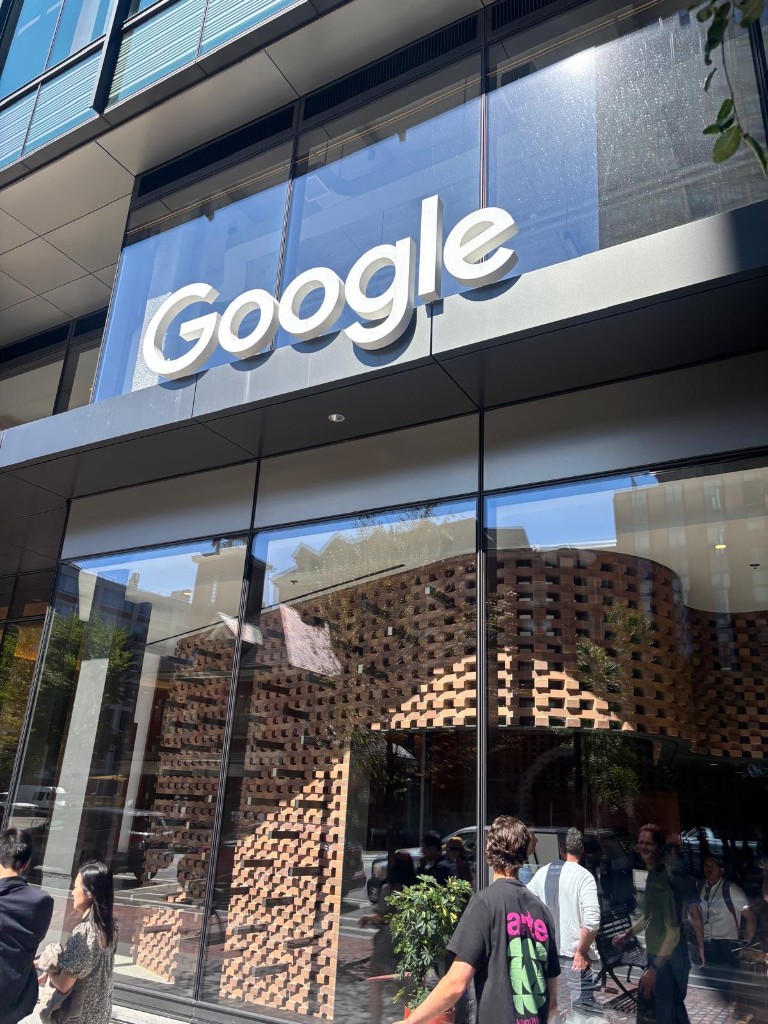 At Google, Boston
A hundred funded startups came together at Google’s office in Boston.
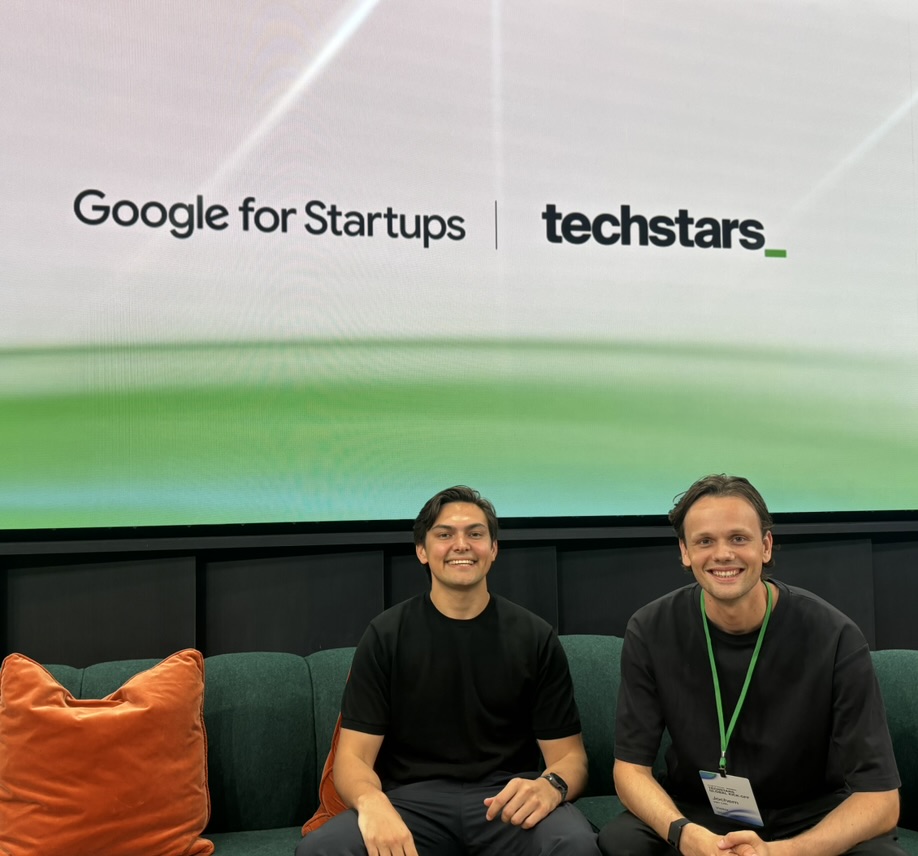 Techstars ABN AMRO backs Umbra
Umbra Ai got into Techstars to redefine risk and compliance for regulated financial firms. We’re building the AI-native GRC: track obligations, monitor controls, assess risks continuously.
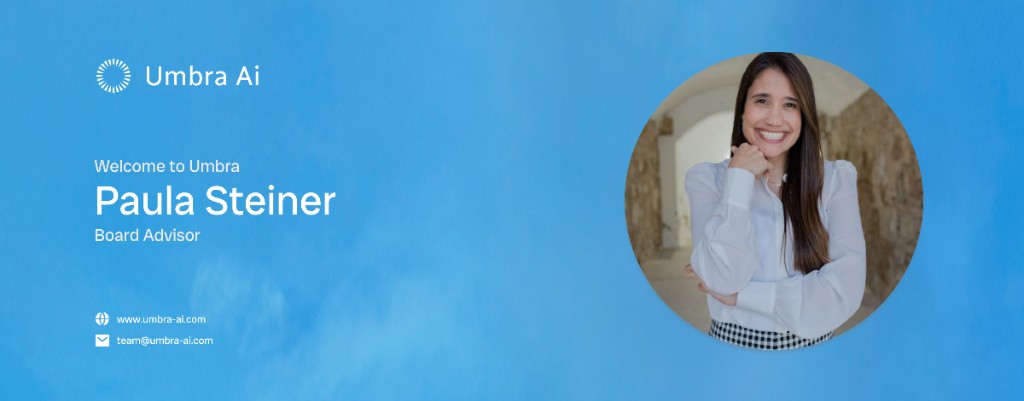 Paula Steiner: Advisory Board
Paula Steiner joins the advisory board, bringing over a decade in compliance, law, and risk across fintech. She joins as we build the agentic operating system for regulated financial firms.


